Who Owns the Security Camera After Installation? The Answer Is Increasingly Complicated
Key Highlights
- Speaking with SecurityInfoWatch at the Axis Communications Partner Summit in Carlsbad, California, Ryan Zatolokin emphasized the shared responsibility for maintaining network-connected security cameras throughout their lifecycles.
- Manufacturers, integrators, end users and IT departments each play a role in ensuring cameras remain properly configured, updated and protected against cybersecurity threats.
- Unclear ownership can create maintenance gaps, particularly when IT and physical security departments follow different policies for software updates and device management.
Installing a network-connected security camera is only the beginning of an ongoing responsibility that can extend years beyond its initial deployment. Keeping that device properly configured, updated and protected requires coordination among manufacturers, systems integrators, physical security departments and IT teams.
But who is ultimately responsible when a camera needs a software update, cybersecurity maintenance or replacement?
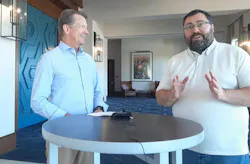
Speaking with SecurityInfoWatch at the recent Axis Communications Partner Summit in Carlsbad, California, Ryan Zatolokin, the company’s senior technologist for North America, discussed the challenges of managing network-connected cameras throughout their operational lives. The annual event brought together more than 500 integration and technology partners to examine industry trends, preview Axis’ product and technology roadmap and explore new developments in physical security.
According to Zatolokin, the answer isn’t necessarily one person or department.
“It’s multiple people,” Zatolokin said.
Manufacturers are responsible for providing software and updates, while integrators oversee installation and initial configuration. End users also have a role because the cameras operate on their networks and must meet their organizations’ cybersecurity requirements.
“So, it’s a collective ownership of this device through its entire lifecycle,” Zatolokin said.
The long-term maintenance gap
One of the biggest challenges, Zatolokin said, is the lack of a long-term maintenance plan once a camera has been installed and configured.
Organizations may establish cybersecurity requirements when devices first connect to their networks, but responsibility for maintaining those devices can become less clear as time passes.
“What happens to that device a year after that, two years after that, five years after that?” he asked.
Some integrators and end users maintain devices throughout their operational lives. Others, he said, have historically taken more of an “out of sight, out of mind” approach.
Zatolokin believes that gap is narrowing as more organizations recognize the importance of lifecycle management.
The consequences of neglected maintenance can extend beyond organizational confusion. Cameras that do not receive necessary software updates may remain exposed to vulnerabilities addressed by subsequent patches. Devices can also remain connected to networks after manufacturers discontinue support, leaving organizations without access to new security fixes.
Zatolokin pointed to the end of manufacturer support as one consideration in determining when a device should be removed from service.
“Maybe the manufacturer is no longer making updates for that device, so it’s not getting cybersecurity patches and so on,” he said.
Organizations need to establish criteria for how long devices remain in service, which policies apply during that period and who is responsible for maintaining them, he said.
Where IT and physical security responsibilities intersect
The growing involvement of IT departments in physical security introduces another consideration: The two groups may operate under different policies for maintaining network-connected equipment.
(In the accompanying video, Axis Communications' Ryan Zatolokin explains who is responsible for keeping security cameras updated when IT and physical security departments follow different maintenance policies.)
Zatolokin said the relationship should be a close partnership, with physical security identifying operational and protection requirements while IT ensures devices comply with organizational cybersecurity policies.
“Security knows what doors need to be secured, what other operational efficiencies need to be looked at, but IT ultimately knows what their cyber policy is, what their IT security policy is,” he said.
Problems can arise when those policies are not aligned.
For example, an IT department may require devices on its network to be updated every six months, while the physical security department follows a different maintenance schedule.
“Who continues to make sure those updates are done?” Zatolokin asked.
If IT manages the devices, its maintenance policies may be implemented consistently. If physical security is responsible, the same requirements may not always be carried out within the expected timeframe.
The challenge, he said, is establishing who has responsibility for implementing those policies over the long term.
Cloud management can simplify maintenance
Cloud-based device management is one way to reduce the administrative work associated with maintaining cameras across an organization.
Zatolokin said cloud platforms can automate software updates based on schedules, apply updates when new versions become available or allow administrators to initiate them manually.
Those capabilities can help security and IT departments establish maintenance policies without requiring personnel to update every camera individually.
“If you go to each device one by one and you try to update it through its web browser, that’s going to be a very, very time consuming practice,” he said.
Device management tools can instead update hundreds of devices in minutes, reducing the time required from both departments.
“And that saves a lot of time. It saves IT time, it saves security time, and I think it makes it much more realistic to address the challenge of maintaining all these devices,” Zatolokin said.
Automation, however, does not eliminate the need for organizations to determine which departments establish maintenance requirements and who is accountable for carrying them out.
What happens when nobody takes responsibility?
Although manufacturers, integrators and end users all have roles in maintaining network-connected cameras, Zatolokin said organizations can still manage those responsibilities effectively when one party takes the lead.
The greater concern is what happens when no one assumes that role.
“When no one takes ownership, nothing happens,” he said.
Zatolokin described that situation as potentially the worst outcome, particularly when devices remain in service without anyone accepting responsibility for their ongoing maintenance.
“I think as long as, even if one party takes the lead in this, that’s still pretty effective in terms of taking care of those devices through their lifetime,” he said.
The underlying issue, he added, is when responsibility remains unassigned.
“But I’d say the gap, the true gap, and I think you exposed it with your question, is when no one wants to own that device. And I think that is, that’s a challenging situation.”
About the Author
 Rodney Bosch
Editor-in-Chief/SecurityInfoWatch.com
Rodney Bosch is the Editor-in-Chief of SecurityInfoWatch.com. He has covered the security industry since 2006 for multiple major security publications. Reach him at [email protected].